
Security Audit & Penetration Testing
Website & Web Application Security Audits and Penetration Testing
A structured security review of your website, application and servers — vulnerabilities found and fixed before someone else finds them.
Find the Weak Points Before an Attacker Does
Most websites are only ever tested for security after they have been hacked. A security audit turns that around: we look for the weaknesses an attacker would use — outdated software, injectable forms, weak access controls, exposed files, misconfigured servers — and fix them while they are still just findings in a report.
Our audits cover the application code, the platform it runs on and the server underneath. You get a plain-English report ranked by real risk, not a 200-page scanner export, and because we are developers we can carry out the fixes as well as recommend them.
What’s Included
What a Security Audit Covers
Application Testing
OWASP Top 10 testing: injection, broken authentication, access control, XSS, CSRF, insecure uploads and business-logic flaws.
Platform & Plugin Review
WordPress, WooCommerce, Shopify apps, Laravel packages and npm dependencies checked for known vulnerabilities and unsafe configuration.
API Security
Authentication, rate limiting, data exposure and authorisation tested on every endpoint, including mobile app APIs.
Server & Hosting Hardening
SSH, firewall, TLS, file permissions, exposed services, backups and patch levels reviewed on Linux, Nginx and Apache servers.
Access & Data Handling
Admin accounts, password policies, two-factor, logging, and how personal and payment data is stored and transmitted.
Prioritised Report & Fixes
Every finding rated by severity with evidence and a fix; we can apply the fixes and re-test to confirm they are closed.
Benefits
Why Have Your Site Audited by Developers
- Findings come with fixes, not just advice — and we can implement them in the same engagement.
- Testing is done safely on staging or with agreed windows, so live customers are never affected.
- A report your management, insurer or enterprise client can read, plus technical detail for developers.
- Re-test included, so you know the issues are actually closed.
- Optional quarterly re-audits and monitoring so new plugins and code changes do not reopen old holes.
Technologies Used for Security Audit & Penetration Testing
We recommend the right tools for your goals, budget and team — never a one-size-fits-all stack.
Discuss Your ProjectHow We Work
Our Security Audit & Penetration Testing Process
Discovery & Consultation
We learn about your business, audience and goals, review any existing website and agree on clear success criteria.
Strategy & Planning
We define the sitemap, features, technology stack and timeline, so scope and budget are clear before work begins.
UI/UX Design
We design wireframes and polished, responsive layouts for your approval, focused on usability and conversions.
Development
We build with clean, standards-based code, integrate your tools and set up an easy-to-use content editor.
Testing & QA
We test functionality, speed, security, accessibility and SEO across browsers and devices before launch.
Launch & Support
We deploy, monitor and fine-tune your site, then provide ongoing maintenance and support as you grow.
FAQ
Security Audit & Penetration Testing FAQs
What is the difference between a security audit and penetration testing?
An audit reviews configuration, code and practices against known good standards. Penetration testing actively tries to exploit weaknesses the way an attacker would. We combine both: the audit finds what is misconfigured, the testing proves what is actually exploitable.
Will testing break my live site?
No. Intrusive tests run against a staging copy or in an agreed maintenance window, and anything that could affect data is done read-only or on a backup. We agree the scope and rules in writing before starting.
A client or insurer has asked for a security assessment. Is this what they mean?
Usually yes. Our report describes scope, method, findings and remediation, which is what supplier questionnaires and cyber-insurance applications typically ask for. If they require a specific standard, tell us and we will align the report to it.
How long does an audit take?
A single website with a standard platform takes about a week from access to report. Larger applications, multiple servers or APIs take two to three weeks. Fixes are quoted separately once you have seen the findings.
Explore More
More Growth & Support Services
Technologies and services that work well alongside security audit & penetration testing.
Website Speed Optimization
Make your website load in a blink. We diagnose bottlenecks and improve Core Web Vitals for better rankings and conversions.
Technical SEO Optimization
Fix the technical foundations of SEO — crawlability, site structure, schema markup and speed — so your content can rank.
Website Maintenance & Support
Proactive updates, backups, monitoring and on-demand fixes that keep your website secure, fast and always online.
Troubleshooting & Bug Fixes
Broken layouts, white screens, plugin conflicts or checkout errors — we diagnose the root cause and fix it properly.
Case Studies & Live Demos
Security Audit & Penetration Testing in Practice
Projects where this work made a measurable difference — the problem, what we built and the results. Each one has a working demo you can try.
- OWASP ZAP
- Burp Suite
- WPScan
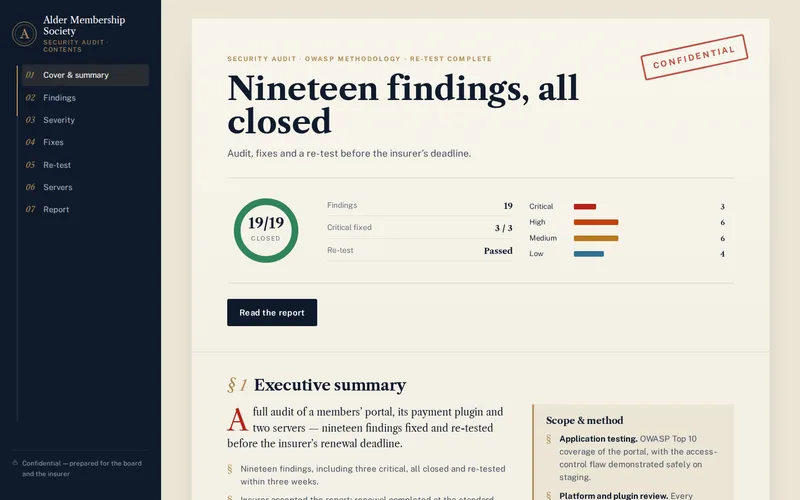
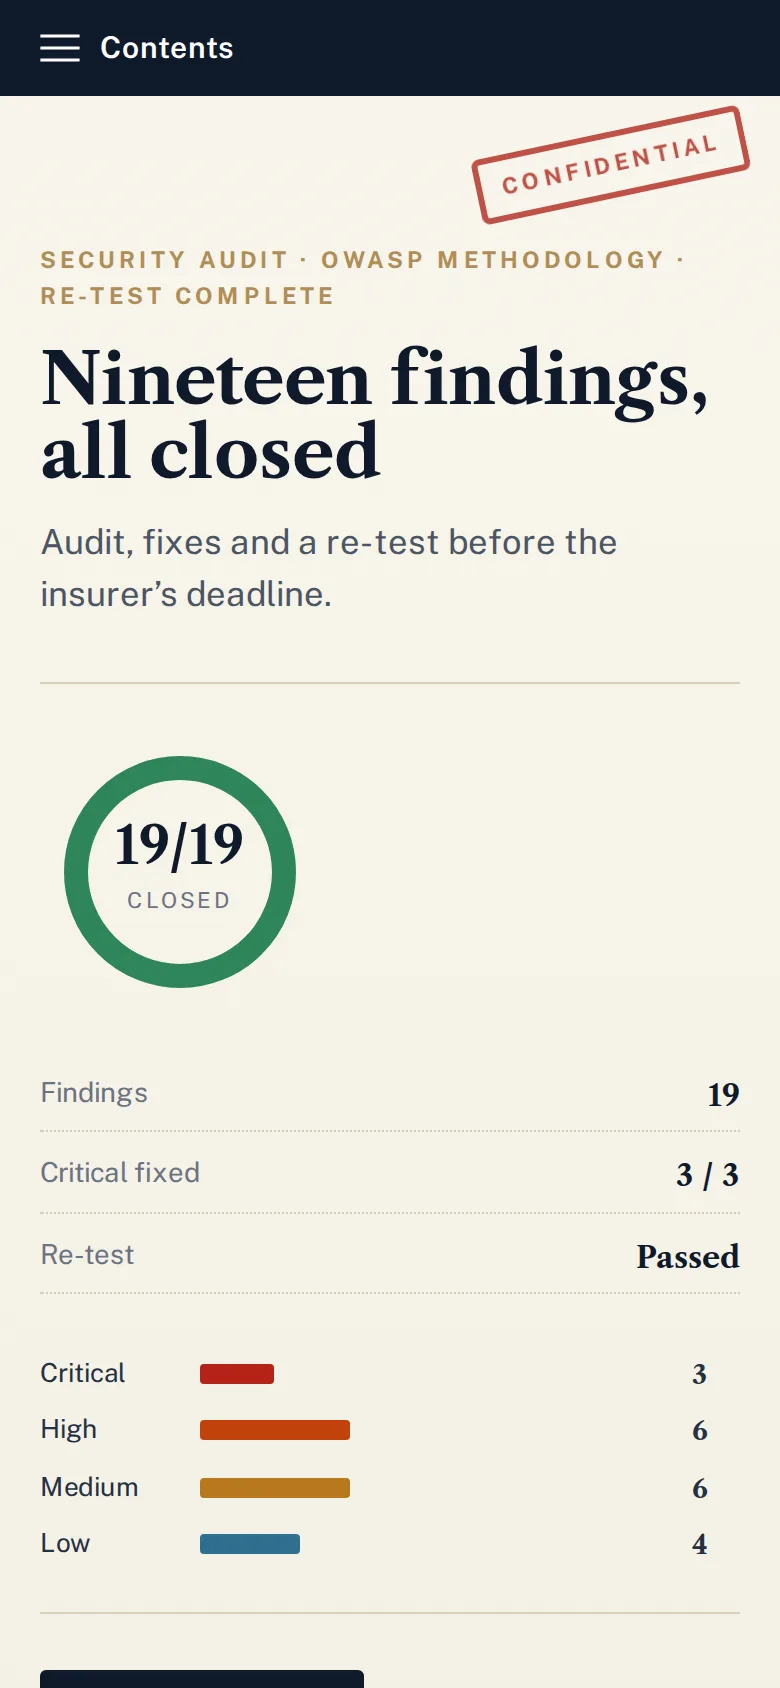
Security Audit
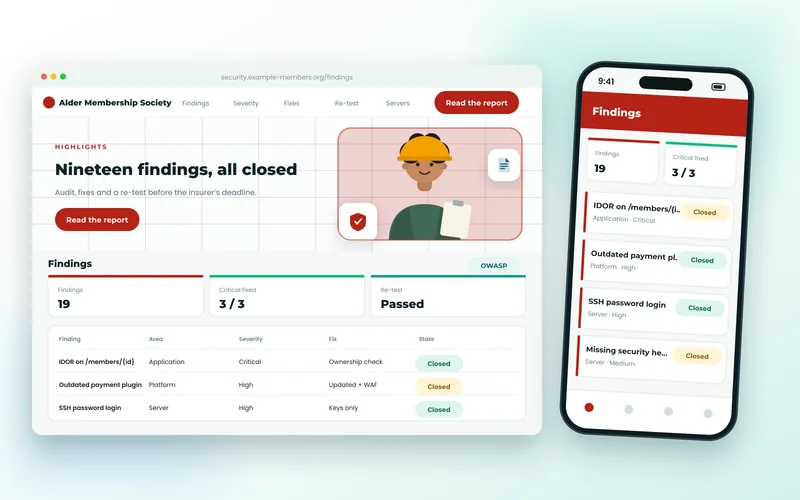
Security Audit & Remediation for a Membership Society
A full audit of a members’ portal, its payment plugin and two servers — nineteen findings fixed and re-tested before the insurer’s renewal deadline.
- Docker
- GitHub Actions
- Nginx
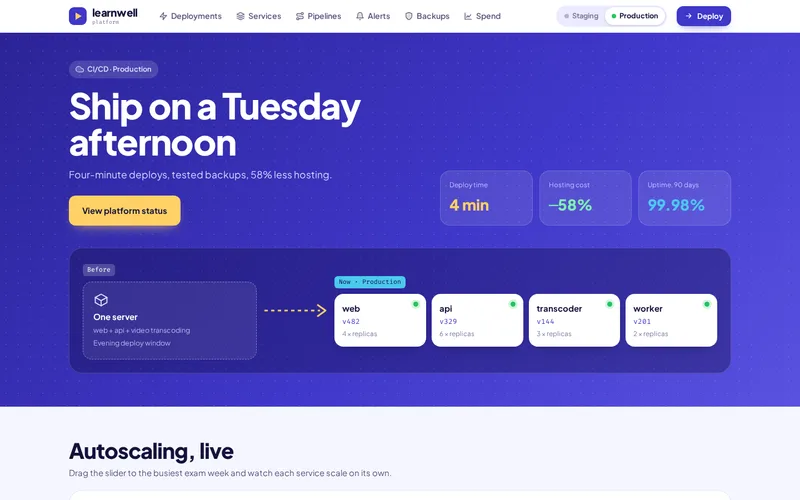
Cloud & DevOps
Learning Platform Cloud Migration
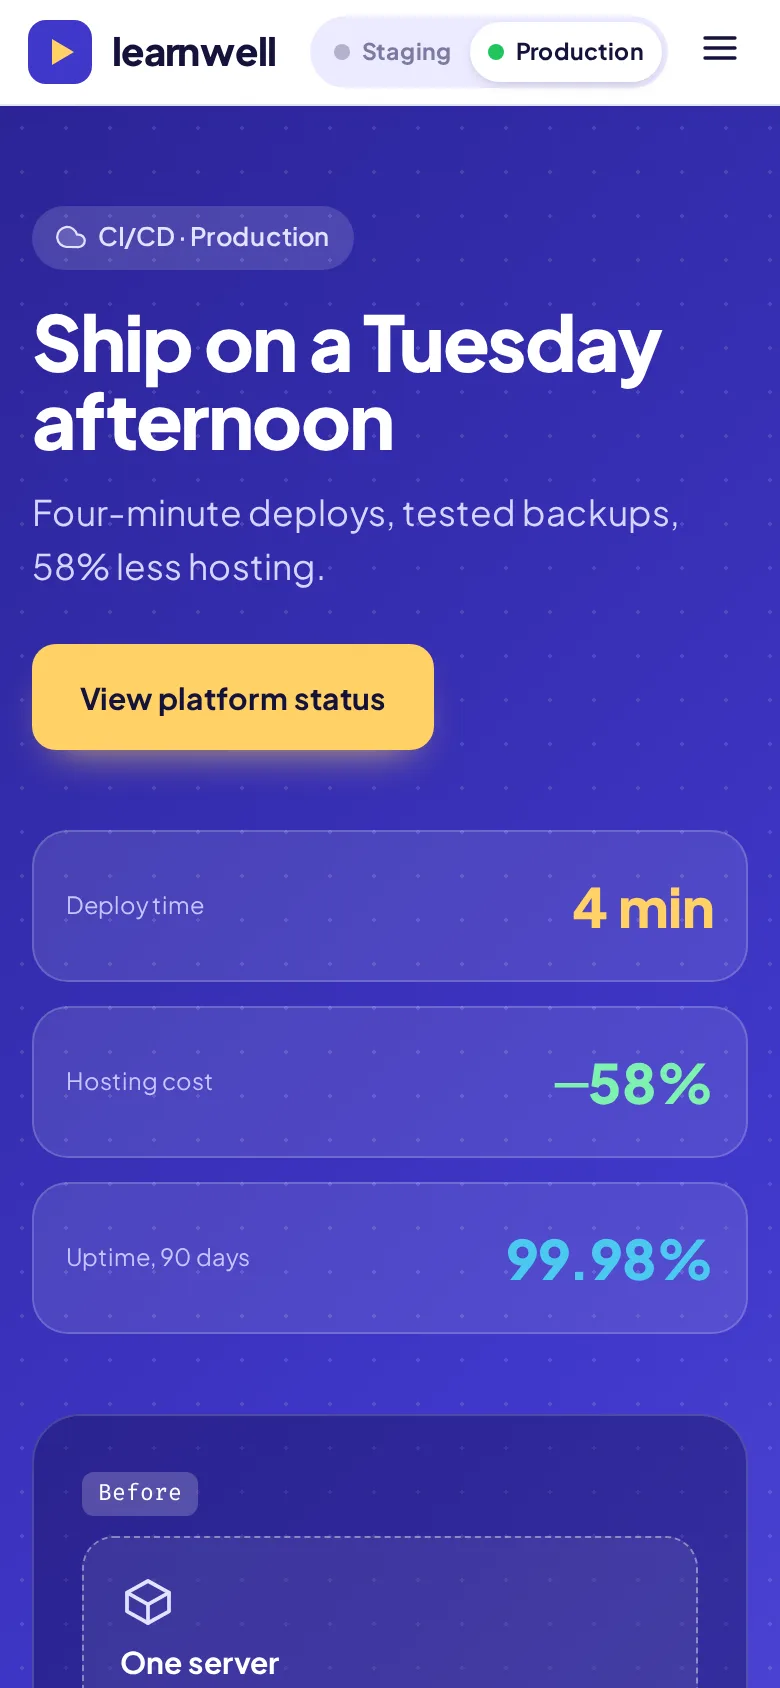
A containerised rebuild of a fragile single-server deployment: 4-minute releases and 58% lower hosting cost.
- CodeIgniter 2 → 3
- PHP 8.3
- Laravel 11
Legacy PHP Modernisation
Trade Supplier Order Desk: CodeIgniter Upgrade & Laravel Migration
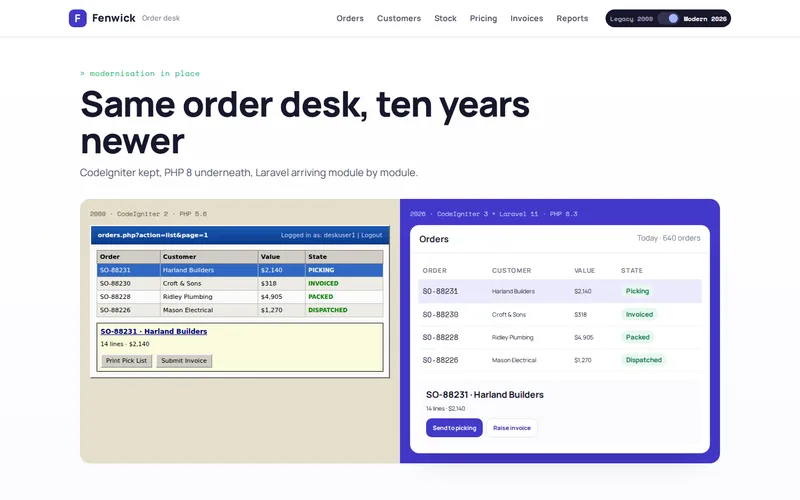
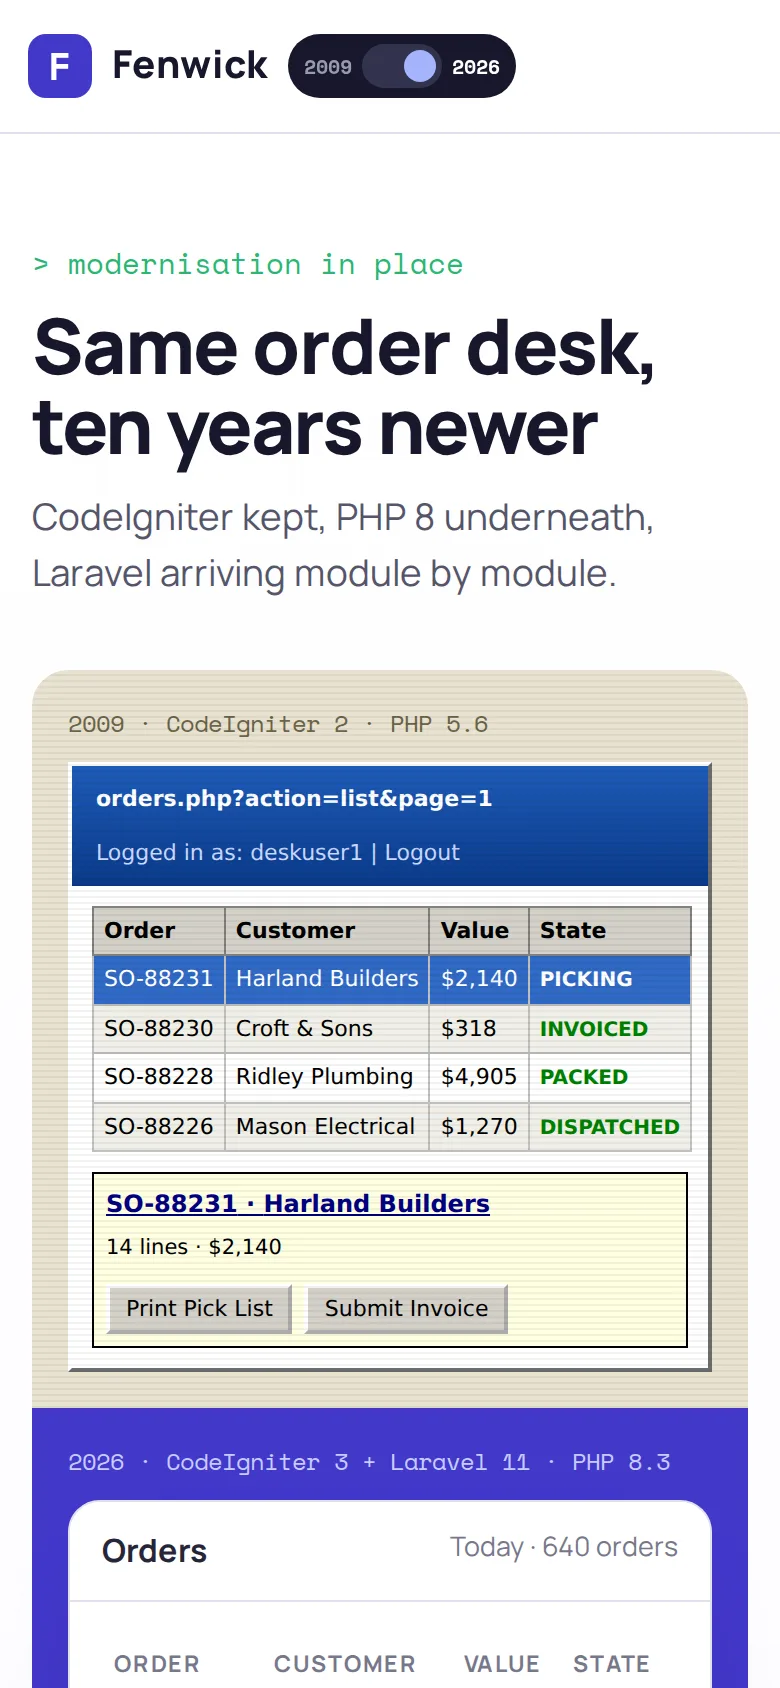
A ten-year-old CodeIgniter order desk brought onto PHP 8, made fast again, and moved to Laravel one module at a time without a day of downtime.
- Azure SQL
- Azure App Service
- Azure Virtual Machines
Cloud Migration
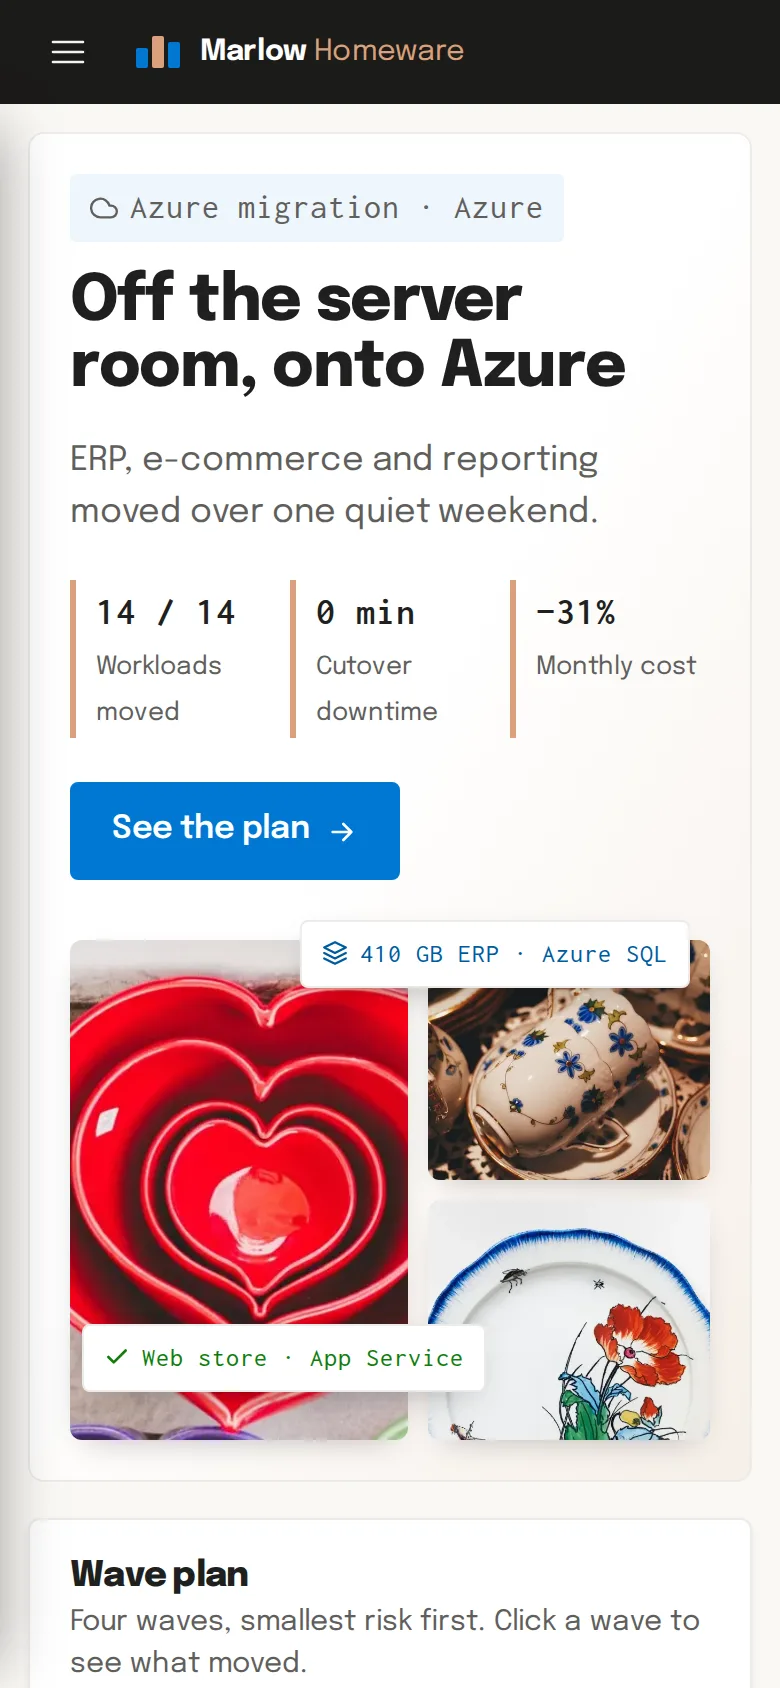
Homeware Retailer: Server Room to Azure
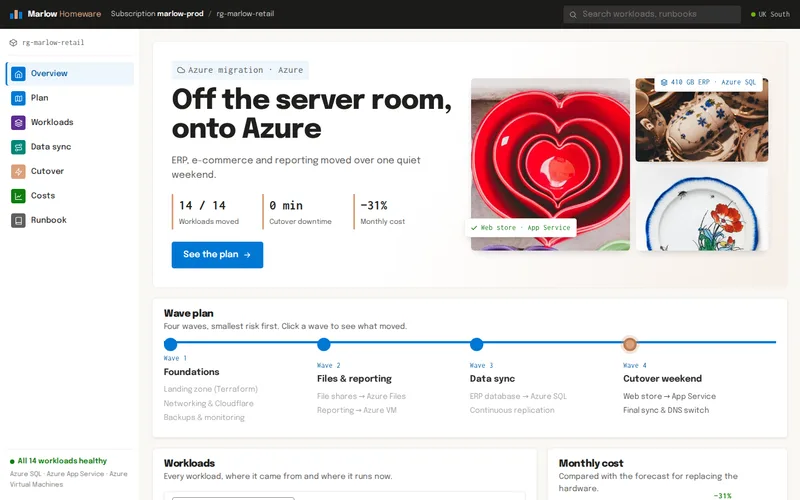
An ERP, a web store, reporting and file shares moved from an ageing server room to Azure over one quiet weekend, with no downtime and a 31% lower monthly bill.
From the Blog
Guides and Comparisons Worth Reading
Straight answers on when this technology is the right choice, what it costs and how to get the most from it.
What a Website Security Audit Actually Covers (and What a Scanner Misses)
An automated scan finds missing headers. An audit finds that any member can read any other member’s data. Here is what a proper security audit looks at, what it produces, and when you need one.
Preparing for a Penetration Test: Scope, Access and What Happens After
Most disappointing penetration tests go wrong before the first request is sent: a vague scope, test logins that do not work, a report nobody has time to act on. Here is how we help clients prepare, what a good report contains, and how fixing and retesting should work.
Firestore Security Rules for Community Apps: Keeping Members' Data Where It Belongs
In a Firebase app, the phone talks to the database directly, so security rules are the only thing standing between one member and everyone else's data. Here is how we design rules around roles, test them before launch, and the mistakes we find most often in community apps.
Security Audit & Penetration Testing Enquiry
Tell Us What Needs Testing
The scope — sites, applications, APIs and servers — determines the time and price.
- Reply within 24 hoursA real person reviews every request.
- Free consultationHonest advice, no obligation.
- 100% confidentialHappy to sign an NDA.
- We review your requirements
- We reply with questions or a call slot
- You receive a clear, itemised proposal