Scoping a Membership Portal Penetration Test
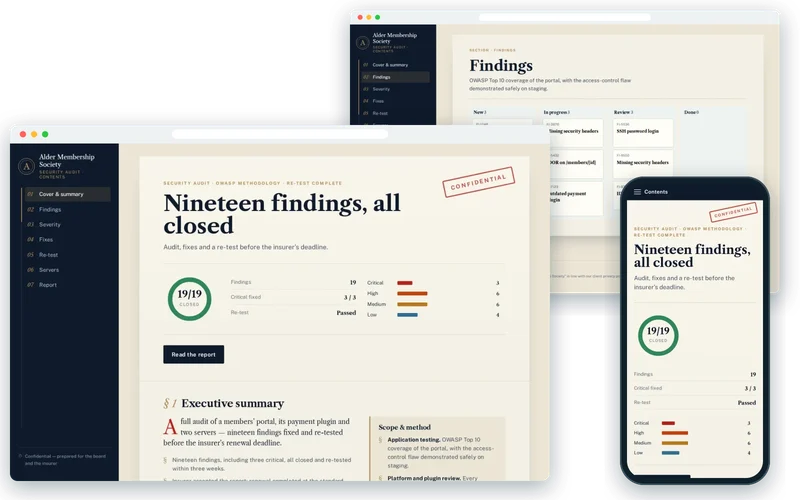
A useful audit starts with an agreed scope. Together with the society we listed every component that touched member data: the portal application, the WordPress site in front of it, the payment integration and the two servers they ran on. Testing took place against a staging copy, while live-server configuration was reviewed read-only, so members were never affected.
Working from a staging copy also meant we could explore more thoroughly. Findings that would have been risky to confirm on a live system could be demonstrated safely, which made the eventual report far more convincing to both the trustees and the insurer.
- Application, CMS, payment integration and servers all in scope
- Testing on staging; production configuration reviewed read-only
- Methodology aligned with the OWASP Top 10